Your AI agents and workflows can act. Guardian decides if they should.
A policy and approval layer between your AI agents, your traditional workflows, and the actions that matter — payments, external sends, irreversible changes — evaluated before they run, not after.
invite-only · every submission read personally by the founder
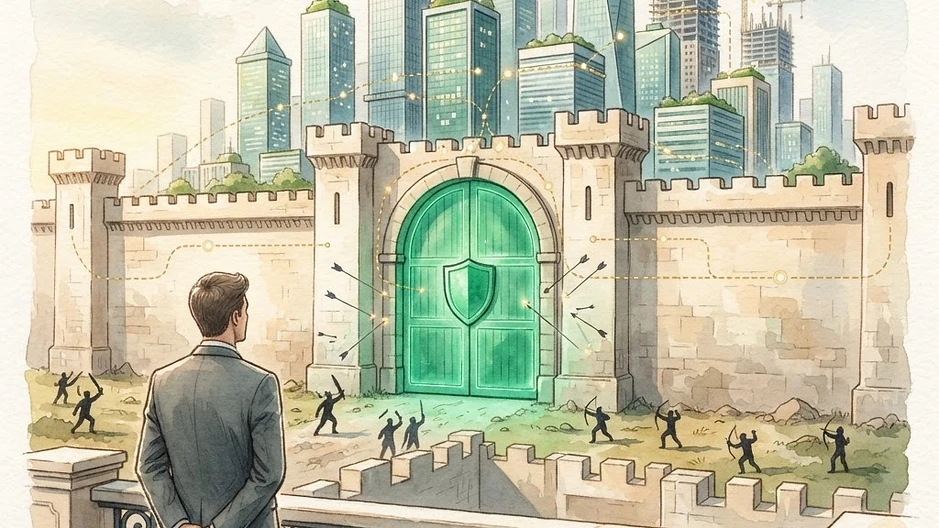
the city thrives behind the wall — the green gate keeps the threats out
Guardian is an authorization layer for consequential actions — whether they come from an AI agent or a plain scheduled workflow. It doesn't replace your workflows — it sits inside them, evaluating every consequential action against your policy and recording the verdict in a tamper-evident log.
Policy, not just permissions
A scoped credential stops the wrong actor. Guardian evaluates the action itself — amount thresholds, recipient allowlists, changed bank details — and decides whether this one should run.
Human approval, before execution
Consequential actions pause for a named human. Not a cleanup job after the workflow fired — a real checkpoint, on the critical path, before anything reaches the destination system.
A record that can't be quietly rewritten
Every decision lands in a hash-chained audit log. Alter a record and verification fails, pointing at exactly which entry broke. Traceable is not the same as provable — Guardian is built for the second one.
Guardian watches,
so you can grow.
You didn't start this business to babysit automations. Guardian stands the watch — so the agents and workflows can do more, and you can sleep at night.
Guardian watches every action
While you run the business, Guardian monitors each consequential move your automations attempt — quietly, constantly, on the critical path.
It guards what you can't afford to lose
Payments, external sends, irreversible changes. The risky ones pause for a human; the out-of-policy ones never leave the building.
So you can grow on it
When the gate is trustworthy, you can automate aggressively. More agents, more workflows, more reach — without the 3am worry.
One checkpoint. Three verdicts. Zero doubt.
Your agent or workflow asks Guardian before acting. Guardian answers with a decision — and writes down exactly why.
Routine actions flow
Everything inside policy runs without friction. Nobody babysits the workflow, and nothing slows down.
Consequential actions pause
Actions crossing your thresholds wait for a named human — before execution, not as a cleanup job after.
Out-of-policy actions stop
Anything outside the rules is blocked outright. It never reaches the destination — and the attempt is on record.
A tamper-evident record
Every decision lands in a hash-chained log. Edit one entry and the chain breaks, pointing at exactly where.
Drops into workflows you already run
An n8n community node, an SDK, and an MCP server. Add a checkpoint to an existing workflow — no rebuild, no migration.
Approval that fits a real team
Organizations, projects, and roles. The right person approves the right thing — your client's finance lead on payments, not whoever happens to be logged in.
Request access
Every submission is read personally. If your use case fits the pilot, we'll reach out directly.
You're on the list
We read every submission personally. If it's a fit, expect a direct email — not a drip campaign.
The core engine is built and tested. We're working with a small group of design partners on real workflows — and you talk to the founder, not a support queue.